Trust & security
What we run on, and what we commit to.
Written for the procurement team, not the marketing page. Where a control is not yet in place, this page says so.
Infrastructure
Where the platform runs
Google Cloud Platform, region us-east4. Compute on Cloud Run; application data in Firestore.
A HIPAA business associate agreement is in place with the cloud provider covering the production project.
Certificates are signed with Ed25519. The public trust anchor is published at a stable address and verification resolves against it directly.
The verification page performs a client-side read against a published projection. No Foster Rx server sits in the verification path, which is what allows verification to remain free and permanent.
Operational events are recorded to a hash-chained append-only log. Agent build sessions are recorded to a separate chained ledger with per-session attribution.
Internal and demonstration surfaces sit behind identity-aware access control with an explicit principal allowlist. Production surfaces are not publicly invocable.
Data handling
What we hold, and what we do not
Two layers, and no vendor feed in the certified corpus
Certified claims derive from primary registry records ingested from issuing authorities, and from Foster Rx internal methodologies. No commercial data feed sits behind a certified claim.
Client material stays yours
Documents supplied for an engagement are used for that engagement. Retention and any secondary use are set in the services agreement, in writing, before work begins.
Assessments are recorded
Every assessment we produce is recorded whether or not it is transmitted, so calibration is measured over everything rather than only over favourable results. Recording is internal; publication is your decision.
Corrections are signed, not deleted
If an assessment is wrong, a superseding certificate is issued and the original stays verifiable. Nothing is quietly withdrawn.
Compliance posture
What we are built to, and where attestation stands
Stated precisely, because a security team will ask precisely.
The platform is operated to the security, availability and confidentiality criteria: documented access control, encryption in transit and at rest, change management through reviewed commits, and an append-only audit substrate. A third-party Type II examination is planned; no attestation report has been issued yet, and none is represented here.
A business associate agreement is in place with the cloud provider covering the production project. The architecture excludes protected health information from the certified corpus by design, which is a stronger statement than a compliance posture: the data is not present to be exposed.
The information security policy is structured against the Annex A control families. Certification is planned rather than held.
Information security policy, incident response plan, editorial content review procedure and funds transfer verification procedure are maintained, versioned, and shared under NDA during procurement.
Google Cloud Platform for compute, storage and identity. A current subprocessor list is provided with the services agreement and updated on change.
Foster Rx Systems Inc. is a Delaware corporation with its principal place of business in Annapolis, Maryland.
If an attestation report is a contracting prerequisite, raise it early. We would rather set an honest timeline at the start than discover a blocker at signature.
Legal
Agreements and policies
Questions from your security team?
Send them directly. They will be answered by the person who built the system.
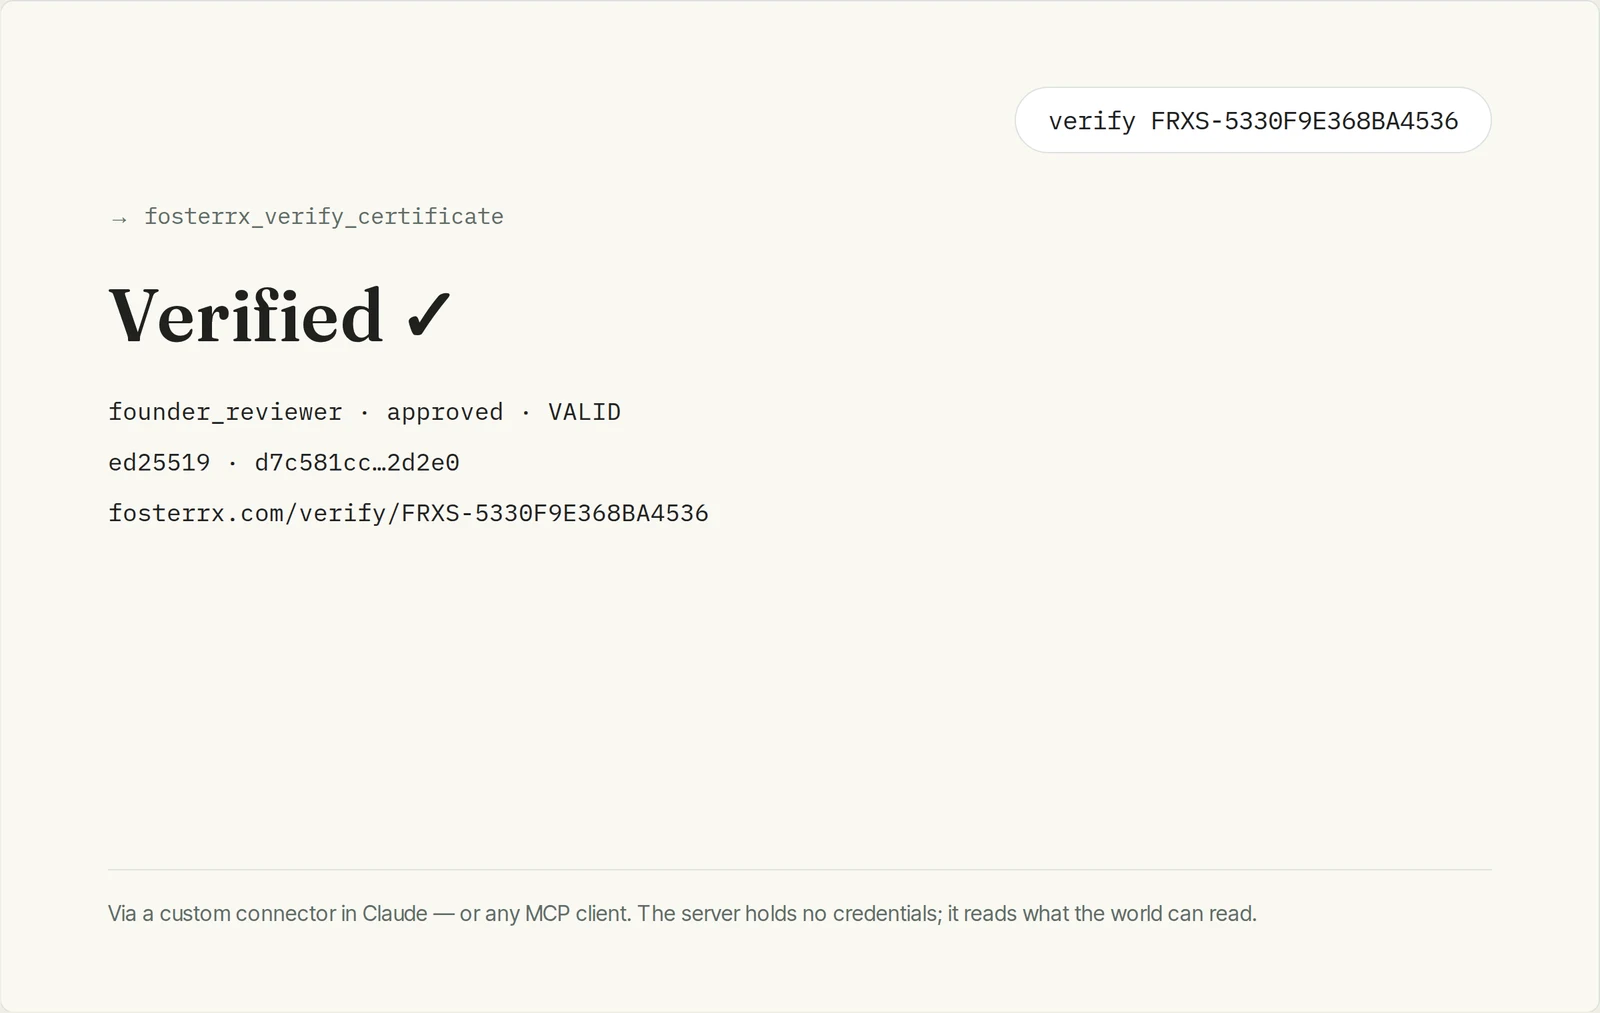
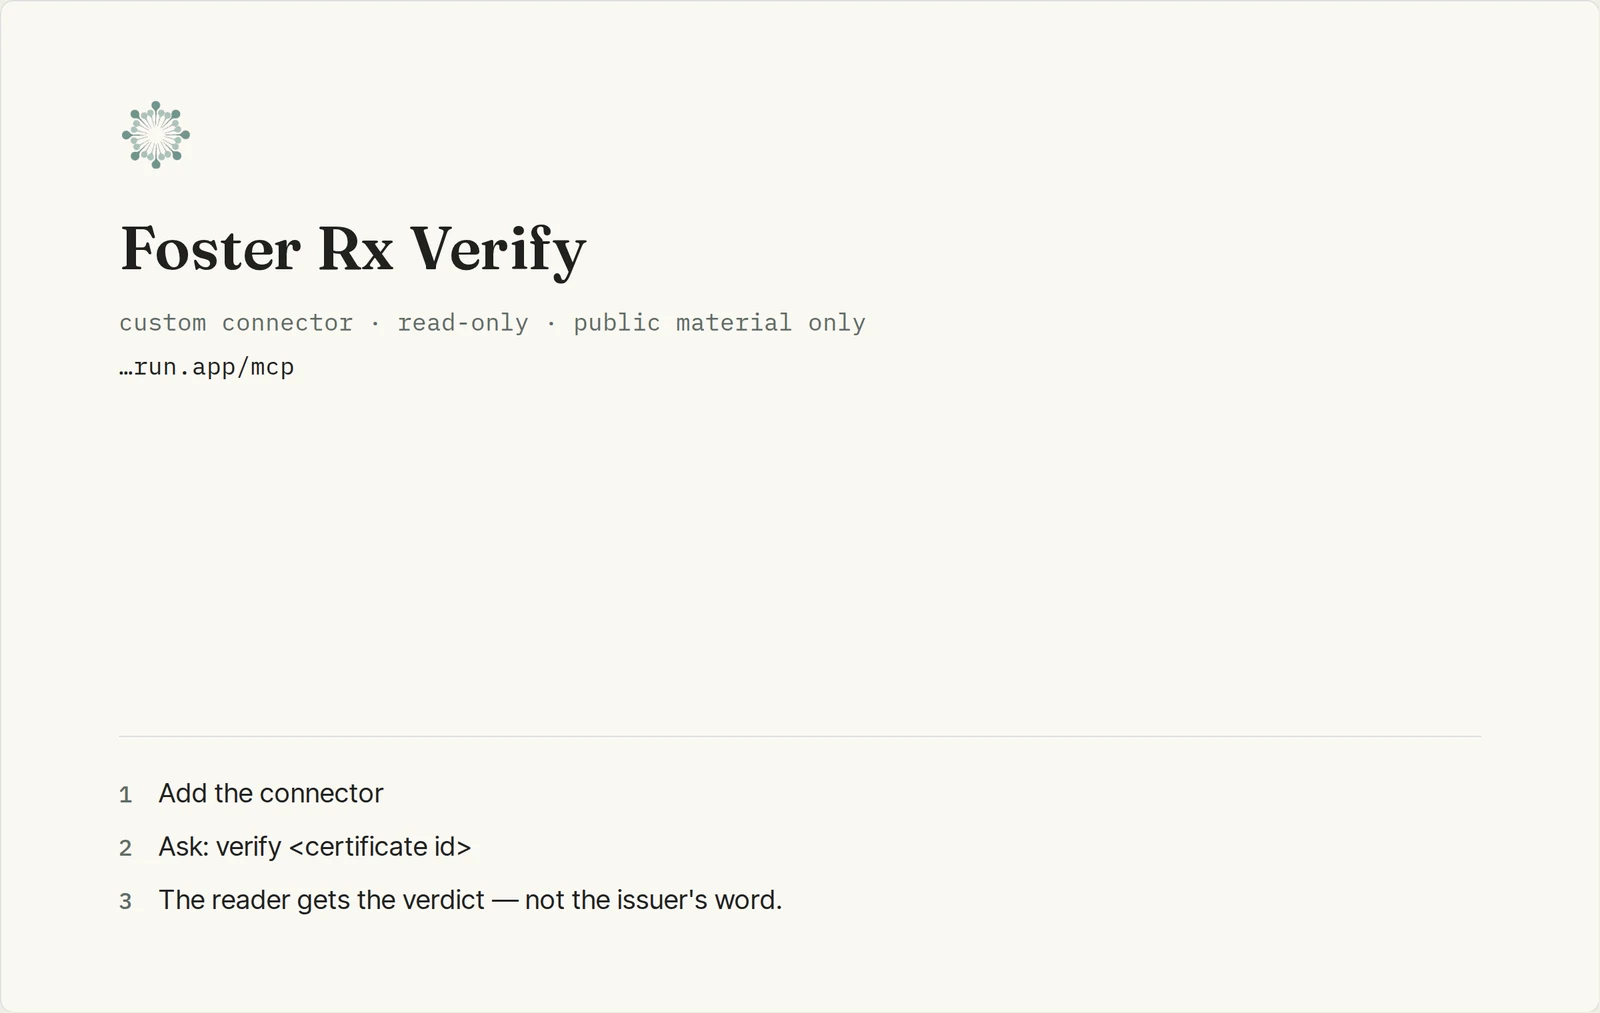
Verify with the AI you already use
The reader gets the verdict. Not the issuer’s word.
Foster Rx Verify is a read-only connector any MCP client can register — it reads the public envelope, fetches the published trust anchor, and runs the cryptography itself. The server holds no credentials, and its source is public.